
“While a number of organizations efficiently blocked the exercise or remediated the vulnerabilities, others skilled compromise, leading to stolen knowledge being printed on the ShinyHunters DLS,” Mandiant mentioned. (DLS is brief for knowledge leak web site.)
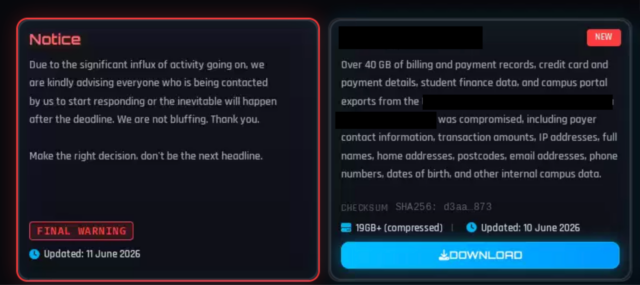
An evaluation of a bash script left within the staging setting exhibits the attackers carried out reconnaissance on compromised organizations, together with mapping the PeopleSoft configurations, viewing course of scheduler, and WebLogic server XML configurations. Eventually, the menace actors established an outbound SSH connection to 176.120.22.24, the IP deal with internet hosting ShinyHunters’ DLS. The stolen knowledge was first compressed utilizing the zstd device. The DLS claimed to have recovered 48GB of knowledge from a single sufferer.
Credit:
Mandiant
{A partially} redacted part of the ShinyHunters’ DLS.
Credit:
Mandiant
ShinyHunters has been lively since at the very least 2019. Over the previous a number of years, it has executed scores of hacks towards a number of the world’s largest firms, affecting tens of millions of individuals downstream. A small pattern of victims consists of Ticketmaster (via the breach of Snowflake, which hosted the info), Spain’s greatest financial institution, Santander, and Salesforce (and, via it, Google and, reportedly, many different firms). ShinyHunters makes use of numerous strategies to achieve preliminary entry, together with exploiting cloud misconfigurations and software program vulnerabilities, stealing OAuth tokens, provide chain assaults, voice phishing, and different types of social engineering.
Mandiant and Rapid7 are offering detailed indicators of compromise. They are additionally advising PeopleSoft clients on the steps they need to take instantly. Given ShinyHunters’ success charge, all PeopleSoft customers would do nicely to heed the calls.


